
I'm preparing for
🎛️ Narrow downsubject · level · topic▾
Results · 7 for “CSRF Protection”
← Front page✨ Smart search: matched by meaning, not just words

⚡ One HLD concept. 60 seconds. Interview ready
Understanding CSRF: Protecting Against Unwanted Requests
CSRF tricks your browser into making requests without your consent.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding SSRF: Server-Side Request Forgery Explained
SSRF is a vulnerability where an attacker tricks a server into making unintended requests.

⚡ One HLD concept. 60 seconds. Interview ready
Secure API Design: 7 Essential Rules for Backend Engineers
Secure API design requires multiple strategies to protect sensitive data and access.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding Cross-Site Scripting (XSS) in Web Security
XSS is a vulnerability that lets attackers run scripts in users' browsers.

⚡ One HLD concept. 60 seconds. Interview ready
Session-Based Authentication: How Cookies & Sessions Work
Session-based authentication uses cookies to remember users after login.

⚡ One HLD concept. 60 seconds. Interview ready
Encryption at Rest vs In Transit: Protecting Your Data
Encryption at rest and in transit are essential for protecting data both stored and in motion.
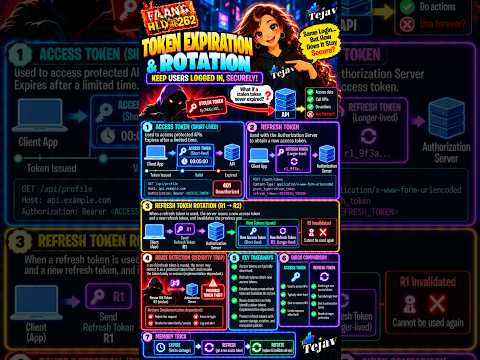
⚡ One HLD concept. 60 seconds. Interview ready
Understanding Token Expiration and Refresh Token Rotation
Token expiration and refresh token rotation secure user sessions by limiting token lifespan and preventing unauthorized access.