
I'm preparing for
🎛️ Narrow downsubject · level · topic2▾
Results · 15 for “Access Control”
← Front page✨ Smart search: matched by meaning, not just words

⚡ One HLD concept. 60 seconds. Interview ready
HLD: Authentication vs Authorization Explained
Authentication verifies who you are, while authorization determines what you can do.

⚡ One HLD concept. 60 seconds. Interview ready
OAuth 2.0: Access Data Without Sharing Your Password
OAuth 2.0 lets apps access user data securely without passwords.

⚡ One HLD concept. 60 seconds. Interview ready
Access Tokens vs Refresh Tokens: How Token Renewal Works
Access tokens are short-lived tokens for API access, while refresh tokens renew them without re-login.

⚡ One HLD concept. 60 seconds. Interview ready
Secure API Design: 7 Essential Rules for Backend Engineers
Secure API design requires multiple strategies to protect sensitive data and access.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding SSRF: Server-Side Request Forgery Explained
SSRF is a vulnerability where an attacker tricks a server into making unintended requests.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding CSRF: Protecting Against Unwanted Requests
CSRF tricks your browser into making requests without your consent.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding CAP Theorem: Trade-offs in Distributed Systems
The CAP Theorem explains the trade-offs in distributed systems during network failures.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding OpenID Connect (OIDC) for Authentication
OpenID Connect allows apps to authenticate users and verify their identities securely.
⚡ One HLD concept. 60 seconds. Interview ready
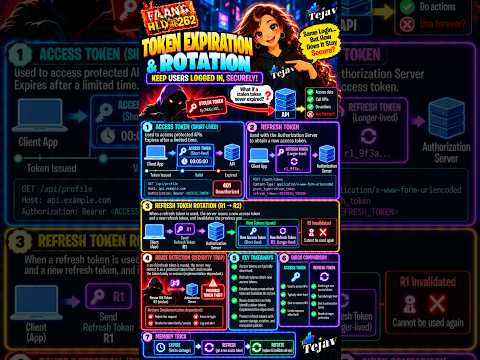
Understanding Token Expiration and Refresh Token Rotation
Token expiration and refresh token rotation secure user sessions by limiting token lifespan and preventing unauthorized access.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding API Keys: Identification and Security
API keys help identify clients and control their access to APIs securely.

⚡ One HLD concept. 60 seconds. Interview ready
Choosing a Distributed Lock: Redis vs Database vs ZooKeeper
Choosing the right distributed lock depends on your system's needs and existing tools.

⚡ One HLD concept. 60 seconds. Interview ready
Optimistic vs Pessimistic Locking in Database Management
Optimistic and pessimistic locking are strategies to manage database access during concurrent transactions.

⚡ One HLD concept. 60 seconds. Interview ready
Kafka Manual Partition Assignment: Using assign() for Control
Kafka's assign() method allows manual control of partition assignments for consumers.

⚡ One HLD concept. 60 seconds. Interview ready
Zero Trust Architecture: Never Trust, Always Verify
Zero Trust Architecture ensures that no user or device is trusted by default.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding Cross-Site Scripting (XSS) in Web Security
XSS is a vulnerability that lets attackers run scripts in users' browsers.