
I'm preparing for
🎛️ Narrow downsubject · level · topic1▾
Results · 31 for “Secure Communication Protocols”
← Front page✨ Smart search: matched by meaning, not just words

⚡ One HLD concept. 60 seconds. Interview ready
HTTP vs HTTPS: Understanding the Key Differences
HTTPS is a secure version of HTTP that encrypts data for safety.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding the TLS Handshake in HTTPS Connections
The TLS handshake establishes a secure connection for HTTPS, ensuring data safety.

⚡ One HLD concept. 60 seconds. Interview ready
Secure API Design: 7 Essential Rules for Backend Engineers
Secure API design requires multiple strategies to protect sensitive data and access.
⚡ One HLD concept. 60 seconds. Interview ready
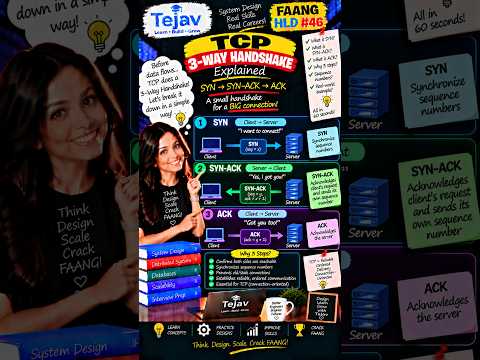
Understanding TCP 3-Way Handshake: SYN, SYN-ACK, ACK
The TCP 3-way handshake ensures reliable connection establishment between a client and server.

⚡ One HLD concept. 60 seconds. Interview ready
Encryption at Rest vs In Transit: Protecting Your Data
Encryption at rest and in transit are essential for protecting data both stored and in motion.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding mTLS: Microservices Authentication Explained
mTLS allows microservices to verify each other's identities using certificates.

⚡ One HLD concept. 60 seconds. Interview ready
Symmetric vs Asymmetric Encryption: Key Differences Explained
Symmetric encryption uses one key, while asymmetric uses a pair of keys for security.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding CSRF: Protecting Against Unwanted Requests
CSRF tricks your browser into making requests without your consent.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding API Keys: Identification and Security
API keys help identify clients and control their access to APIs securely.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding SSRF: Server-Side Request Forgery Explained
SSRF is a vulnerability where an attacker tricks a server into making unintended requests.

⚡ One HLD concept. 60 seconds. Interview ready
HLD: 5 Microservices Communication Patterns Explained
Microservices can communicate using five key patterns based on their needs.

⚡ One HLD concept. 60 seconds. Interview ready
Protobuf and Schema Evolution: Avoid Breaking Changes
Protobuf schema evolution requires careful changes to avoid breaking existing clients.

⚡ One HLD concept. 60 seconds. Interview ready
HLD: Understanding REST, RPC, and gRPC Differences
REST, RPC, and gRPC are different methods for communication in software systems.

⚡ One HLD concept. 60 seconds. Interview ready
Zero Trust Architecture: Never Trust, Always Verify
Zero Trust Architecture ensures that no user or device is trusted by default.

⚡ One HLD concept. 60 seconds. Interview ready
Session-Based Authentication: How Cookies & Sessions Work
Session-based authentication uses cookies to remember users after login.

⚡ One HLD concept. 60 seconds. Interview ready
Hashing vs Encryption: Key Differences Explained
Hashing is one-way for verification, while encryption is two-way for confidentiality.

⚡ One HLD concept. 60 seconds. Interview ready
HLD — KMS Explained 🔐 What If Your Encryption Key Gets Stolen?
KMS securely manages encryption keys to protect data from theft.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding CAP Theorem: Trade-offs in Distributed Systems
The CAP Theorem explains the trade-offs in distributed systems during network failures.

⚡ One HLD concept. 60 seconds. Interview ready
Container Networking: How Do Containers Communicate?
Container networking enables communication between services in different containers.

⚡ One HLD concept. 60 seconds. Interview ready
HLD: Password Hashing and Salt Explained
Password hashing with unique salts ensures security by creating different hashes for identical passwords.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding OpenID Connect (OIDC) for Authentication
OpenID Connect allows apps to authenticate users and verify their identities securely.
⚡ One HLD concept. 60 seconds. Interview ready
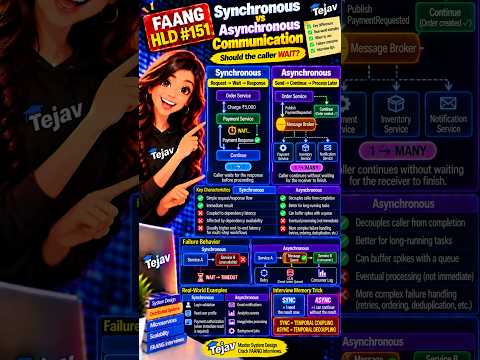
HLD: Synchronous vs Asynchronous Communication Explained
Synchronous communication waits for a response, while asynchronous continues without waiting.

⚡ One HLD concept. 60 seconds. Interview ready
OAuth 2.0: Access Data Without Sharing Your Password
OAuth 2.0 lets apps access user data securely without passwords.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding gRPC Architecture: Behind the Call
gRPC allows efficient communication between services using a structured request-response model.

⚡ One HLD concept. 60 seconds. Interview ready
Paxos Consensus: Understanding Distributed Agreement
Paxos is a protocol that helps distributed systems agree on one value despite failures.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding JWT Authentication: How JSON Web Tokens Work
JWTs allow secure user authentication without needing session storage.

⚡ One HLD concept. 60 seconds. Interview ready
FAANG HLD 🔥 | Raft vs Paxos — What's the Difference? Consensus Explained! ⚡
Raft and Paxos are protocols that help computers agree on values in distributed systems.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding Unary vs Streaming RPC in gRPC
gRPC supports four communication patterns: Unary, Server Streaming, Client Streaming, and Bidirectional Streaming.

⚡ One HLD concept. 60 seconds. Interview ready
Understanding Network Partitions in Distributed Systems
Network partitions occur when servers are operational but can't communicate, affecting system performance.
⚡ One HLD concept. 60 seconds. Interview ready
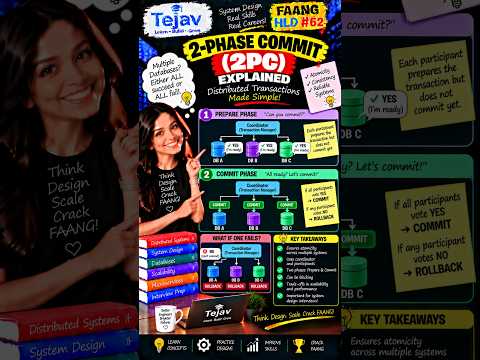
Understanding 2-Phase Commit in Distributed Transactions
2-Phase Commit helps maintain data consistency in transactions across multiple databases.
⚡ One HLD concept. 60 seconds. Interview ready
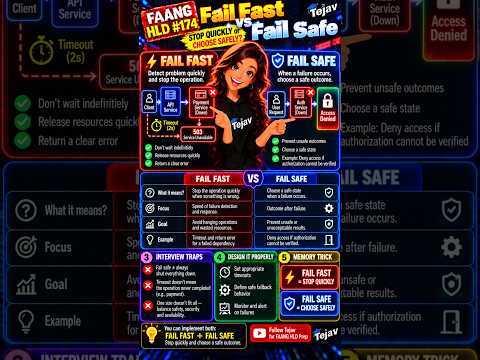
HLD: Fail Fast vs Fail Safe in System Design
Fail Fast means stopping quickly on errors, while Fail Safe ensures safety in failures.